Skip to content
Bijstaan

GLPI Vuln

glpi-vuln

Vulnerability and patch exposure derived from the software inventory already in GLPI. No agent, no scanner, no probing.

version
0.1.0
requires
GLPI 11.0
plugin key
glpivuln
licence
GPL-3.0-or-later
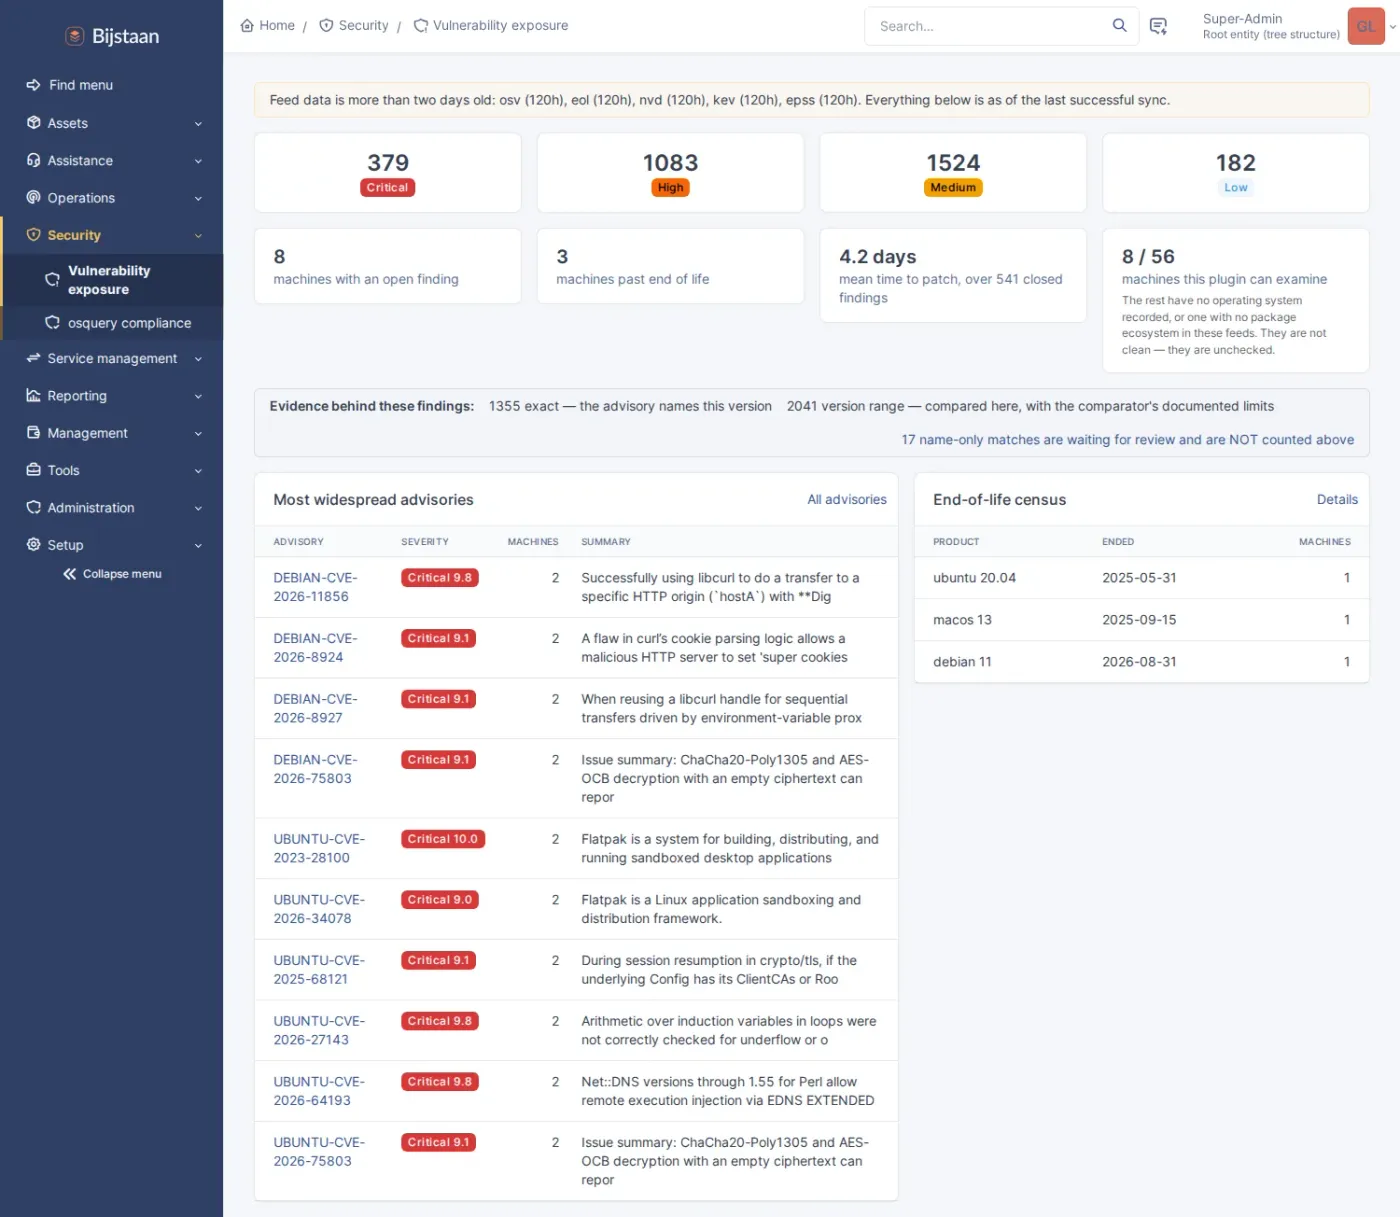
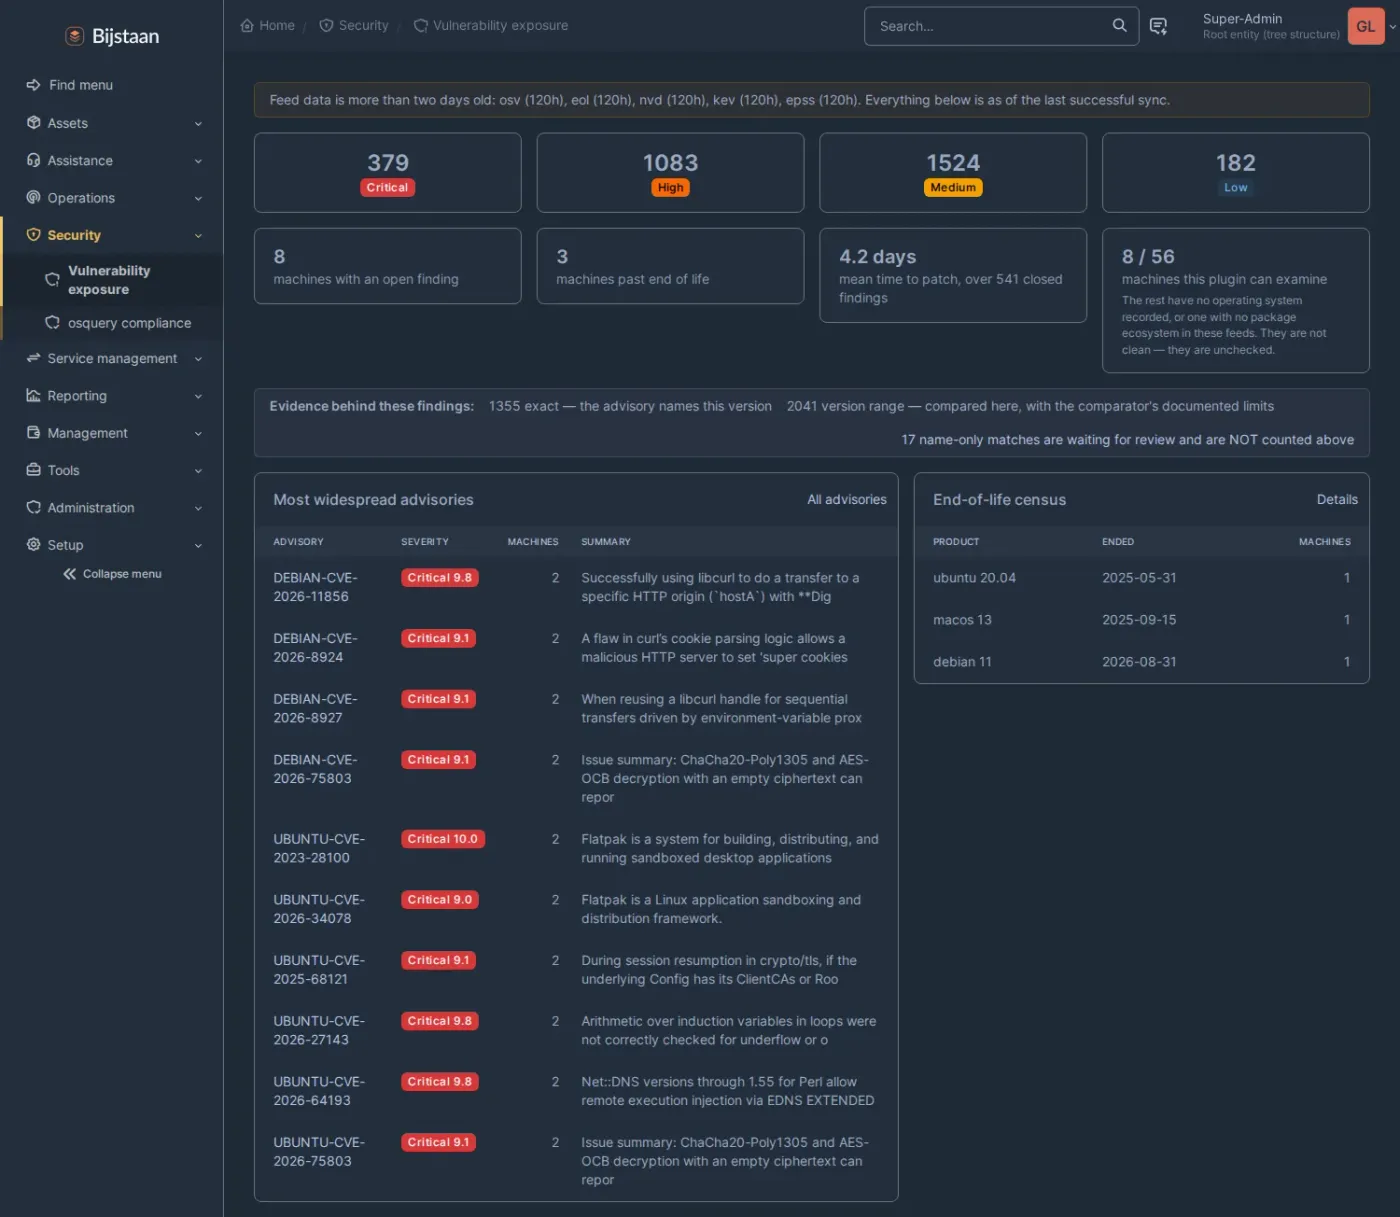
Exposure dashboard: severity tiles, affected machines, mean time to patch, coverage fraction and confidence mix

What it does

  • Sees the laptop that is switched off, which a scan window cannot
  • Every match carries a confidence tier, and the weakest never becomes a finding
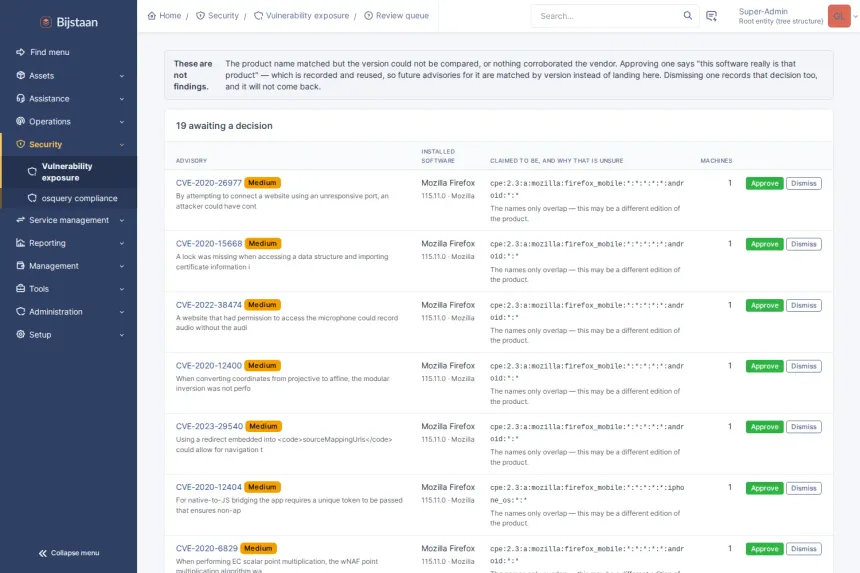
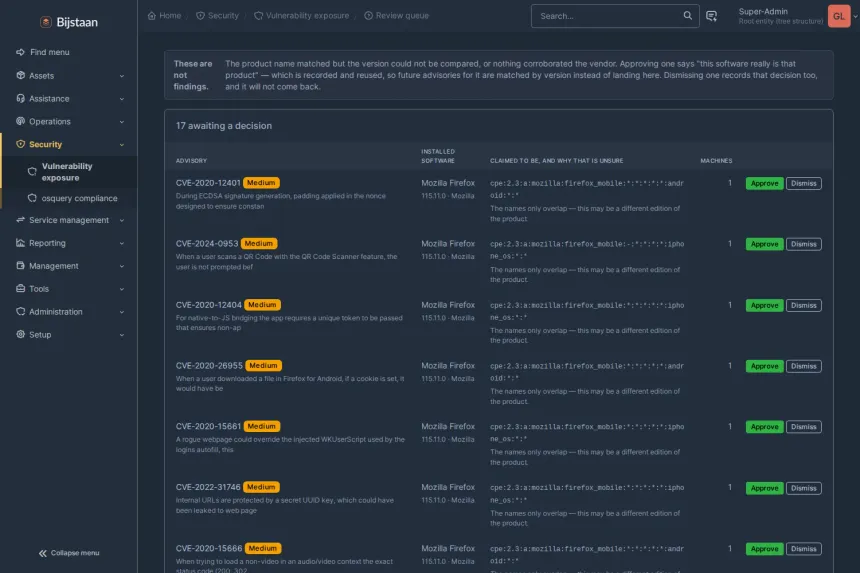
  • A review queue designed to empty — approving teaches the next hundred advisories
  • Leads with coverage and the confidence mix, not a reassuring total
11 more screens

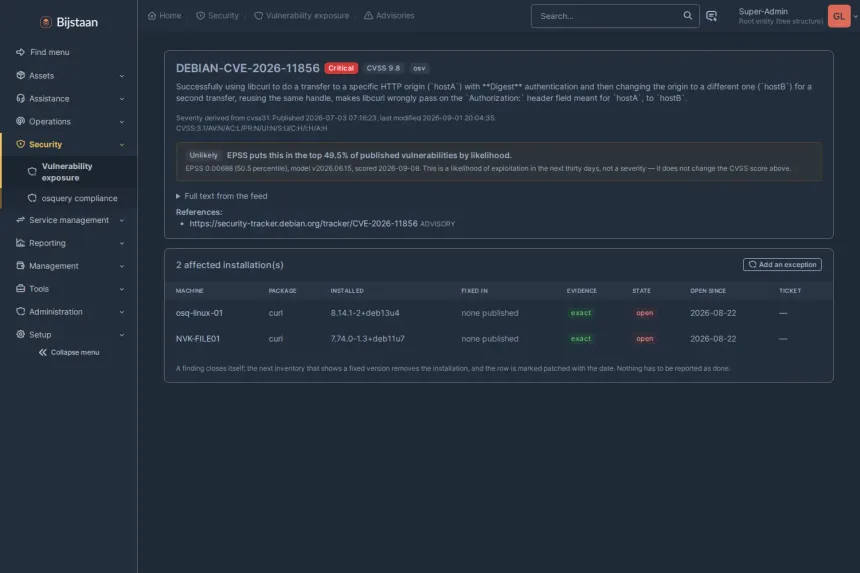
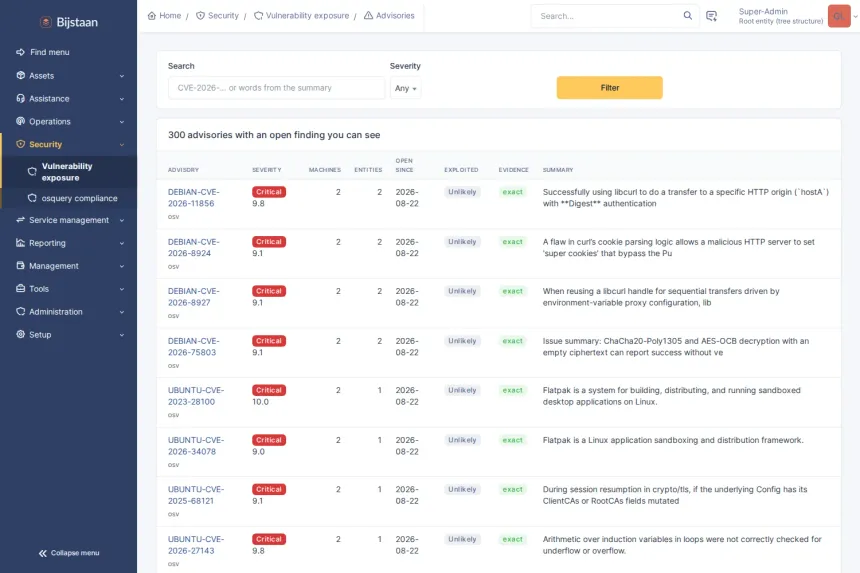
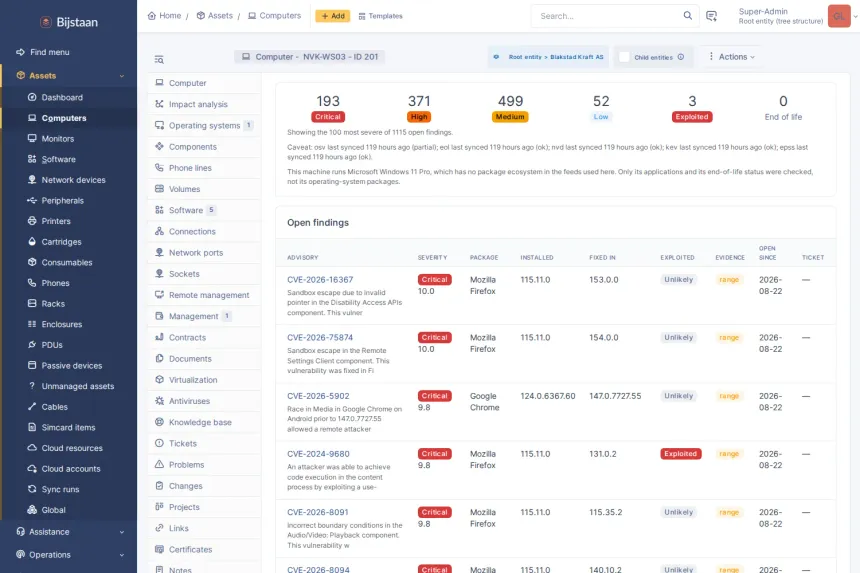
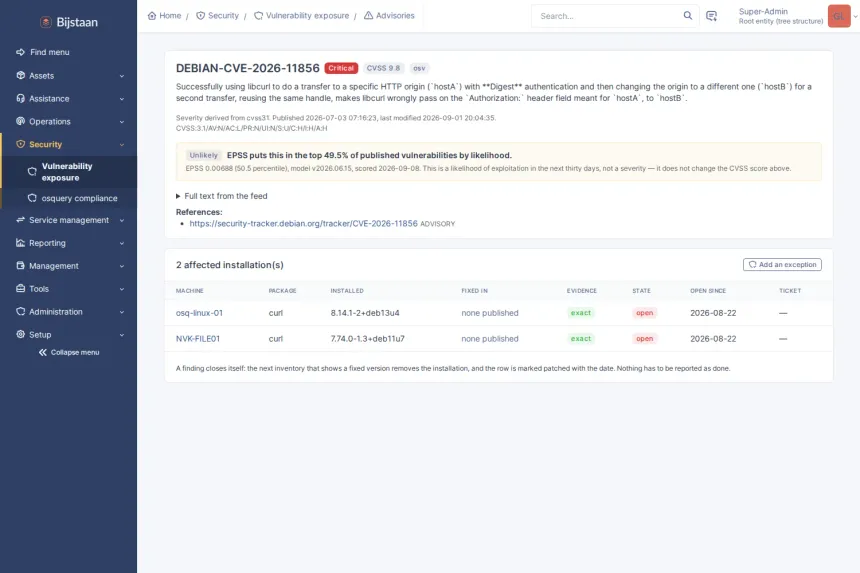
An advisory with the feed's text and references, and every affected installation with package, installed version, fix version, confidence tier and exposure clock
Review queue: name-level matches with the software, the claimed CPE product, machines affected, why it is unsure, Approve/Dismiss
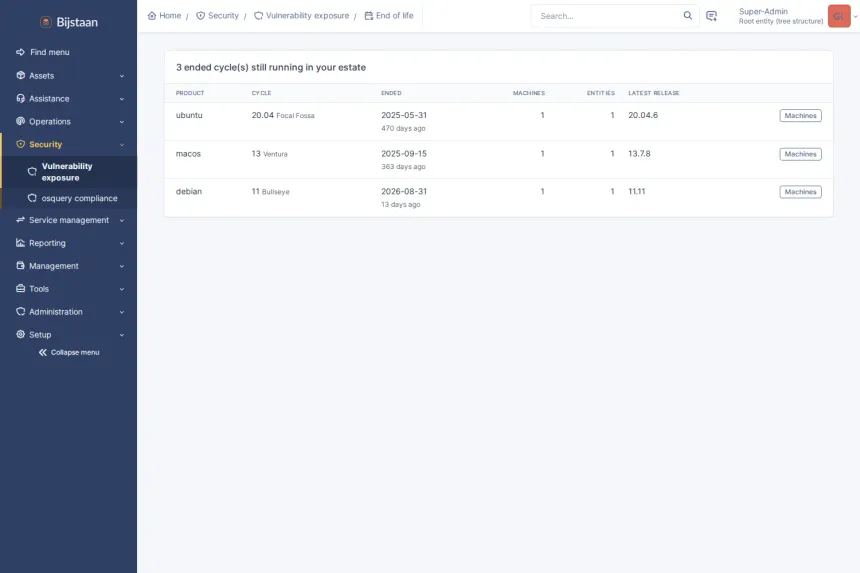
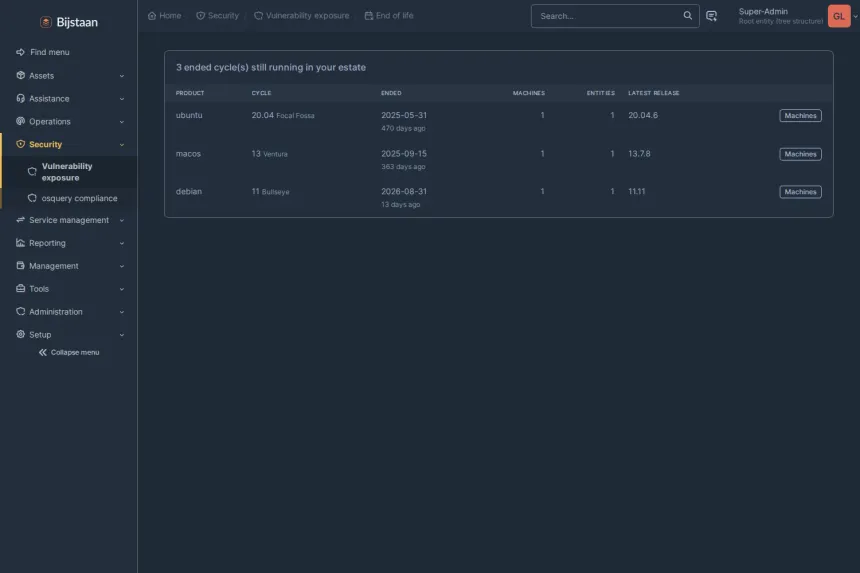
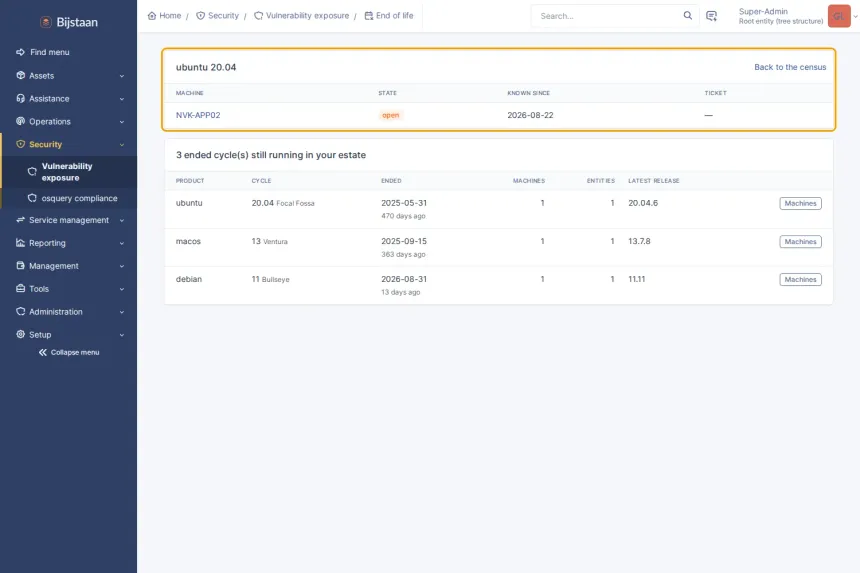
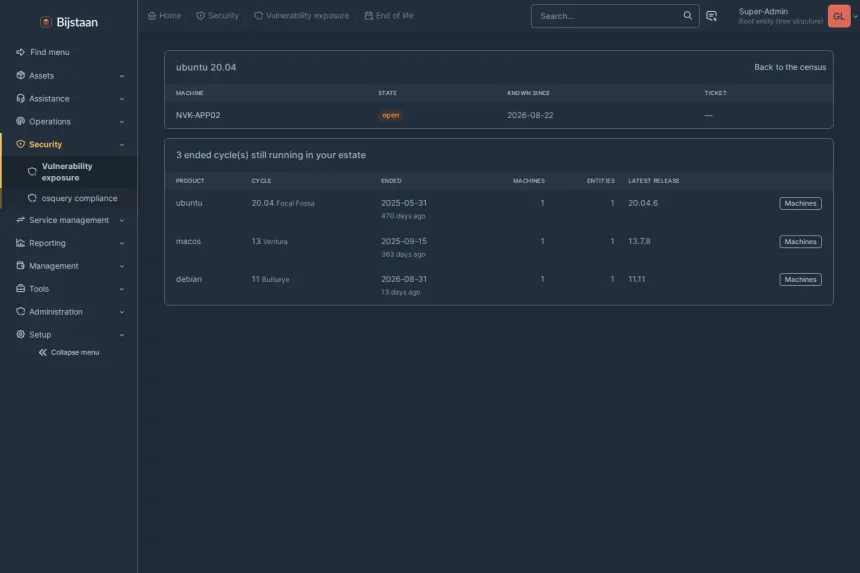
End-of-life census: product, cycle, when support ended, machines and entities affected, latest release
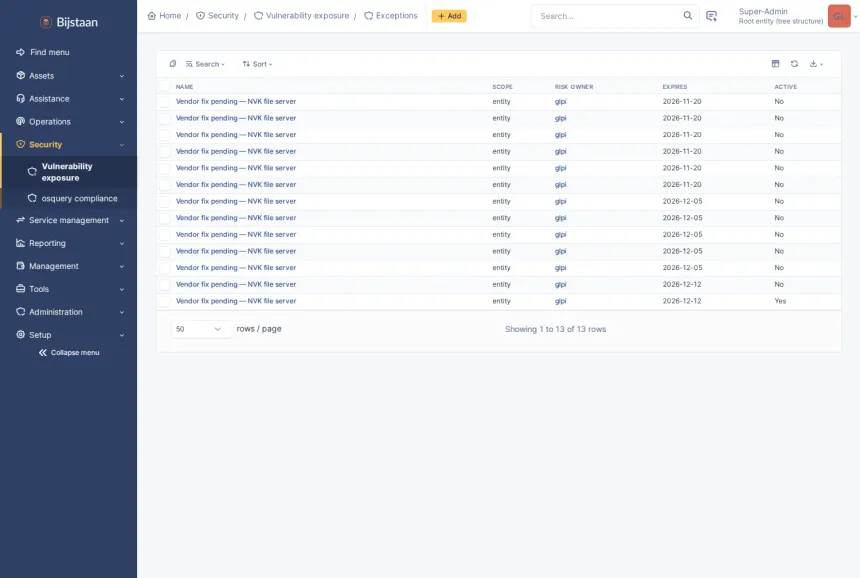
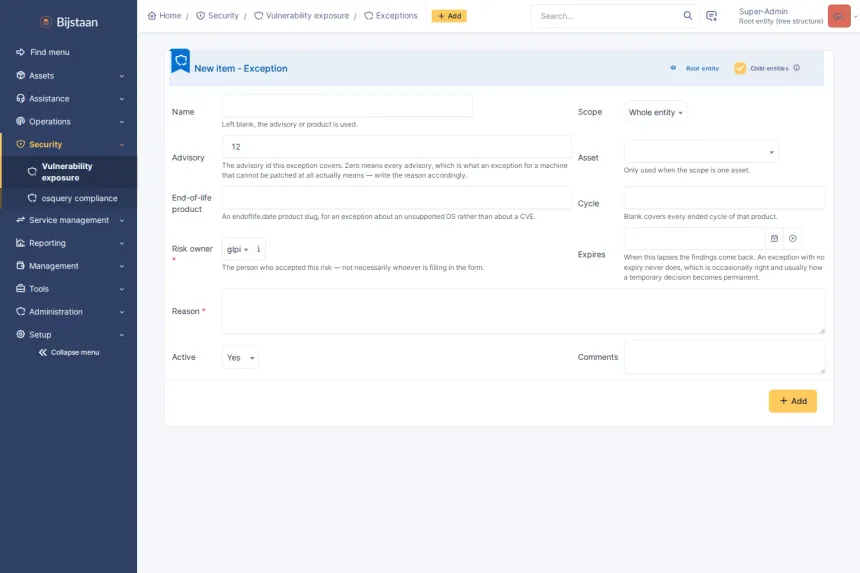
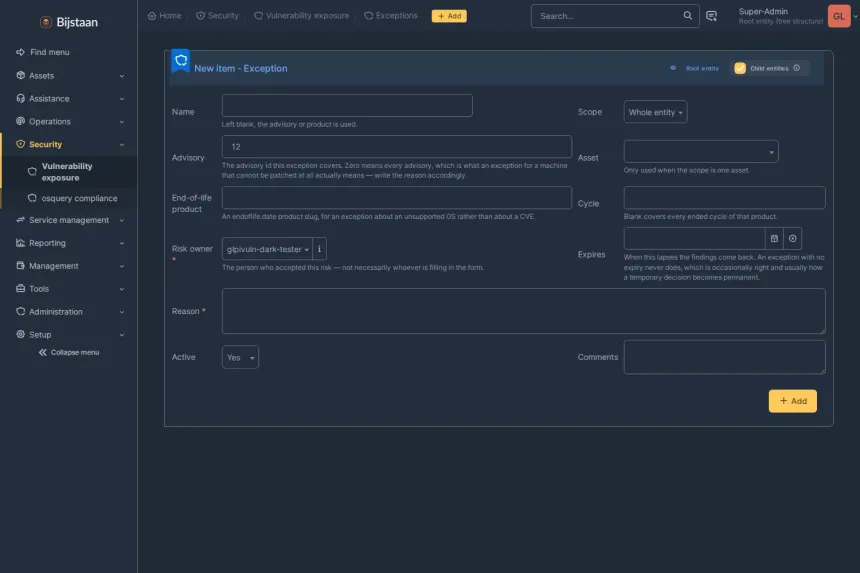
Exception register with scope, risk owner, expiry and state
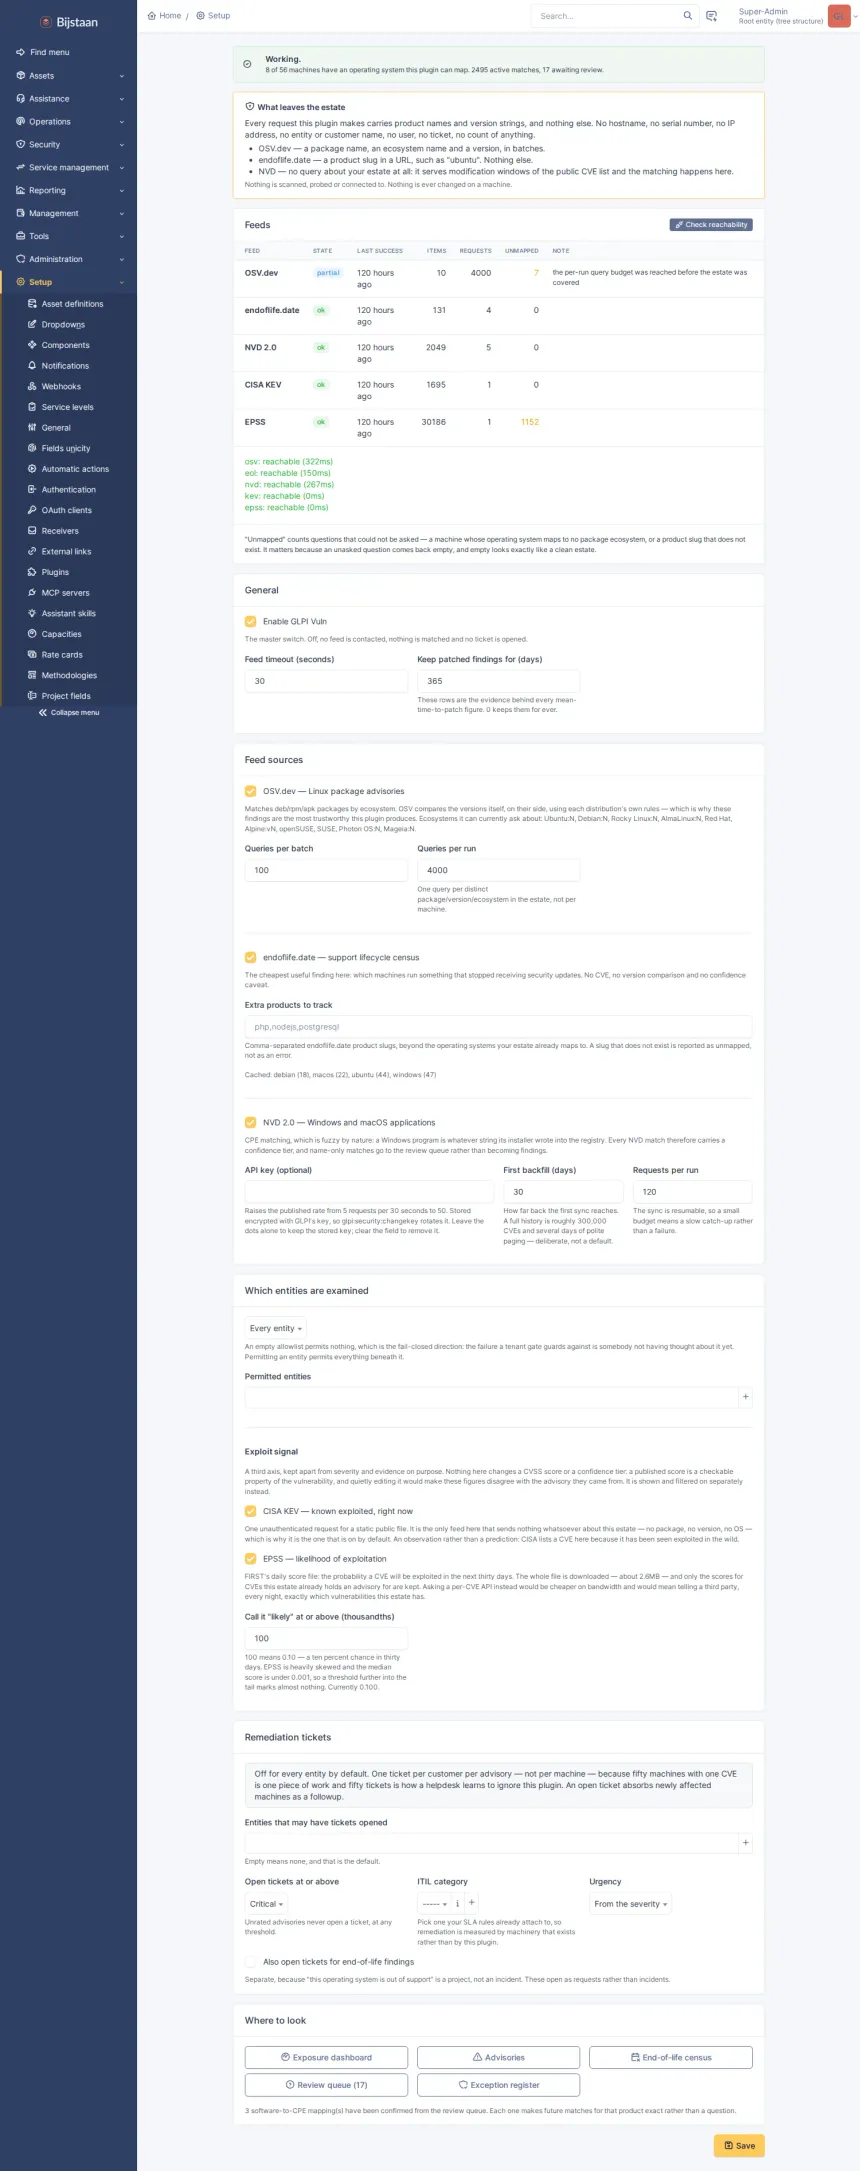
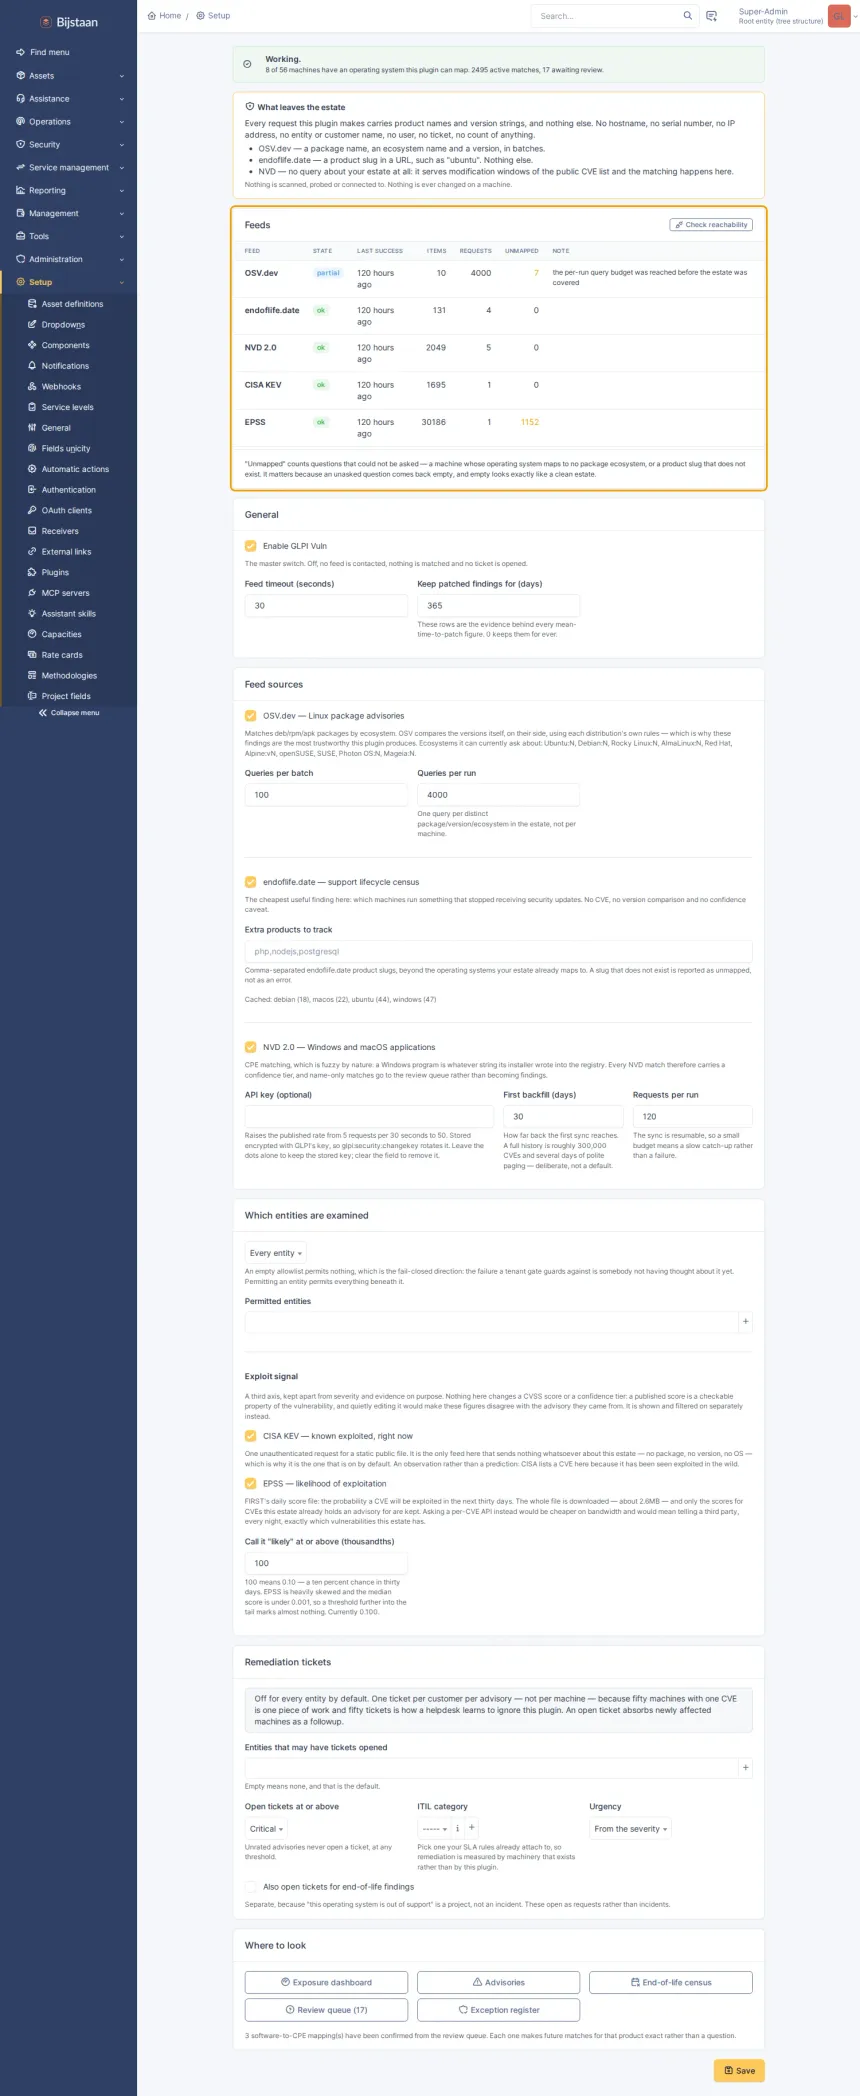
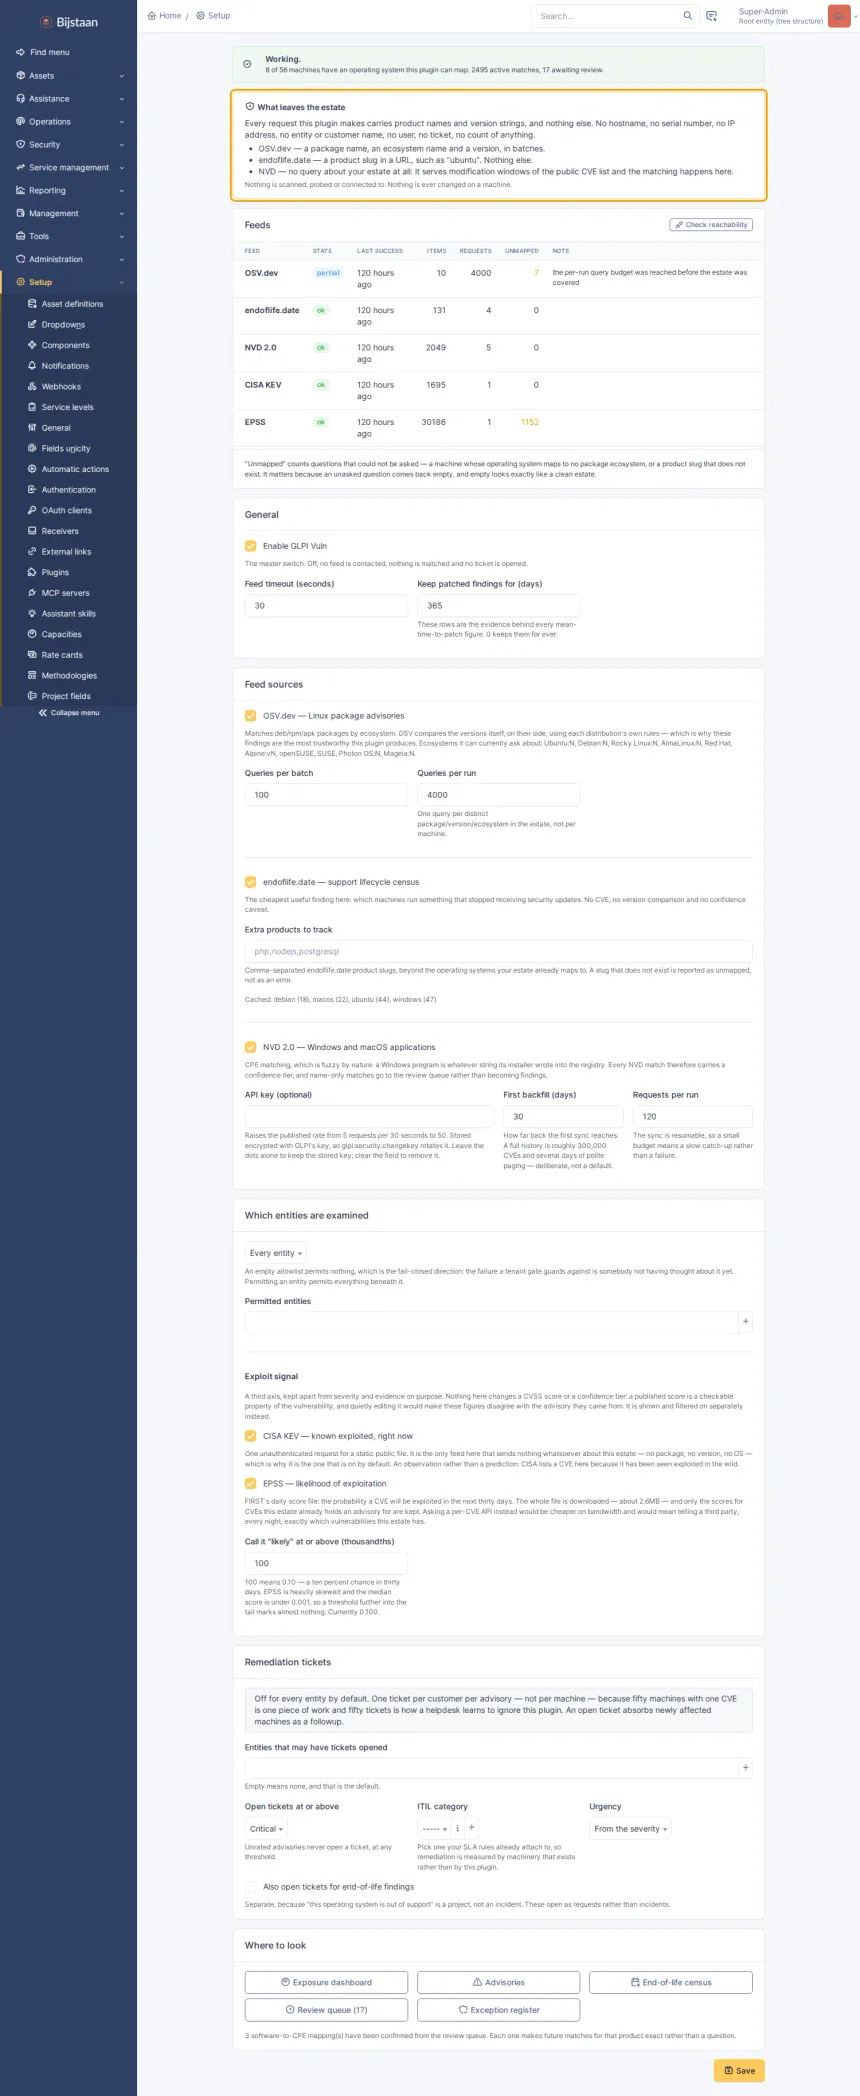
Settings page: status card, what leaves the estate, per-feed table with last run, item counts and unmapped count
Vulnerability and patch exposure derived from the software inventory already in GLPI. No agent, no scanner, no probing.